
A working file, not a whitepaper
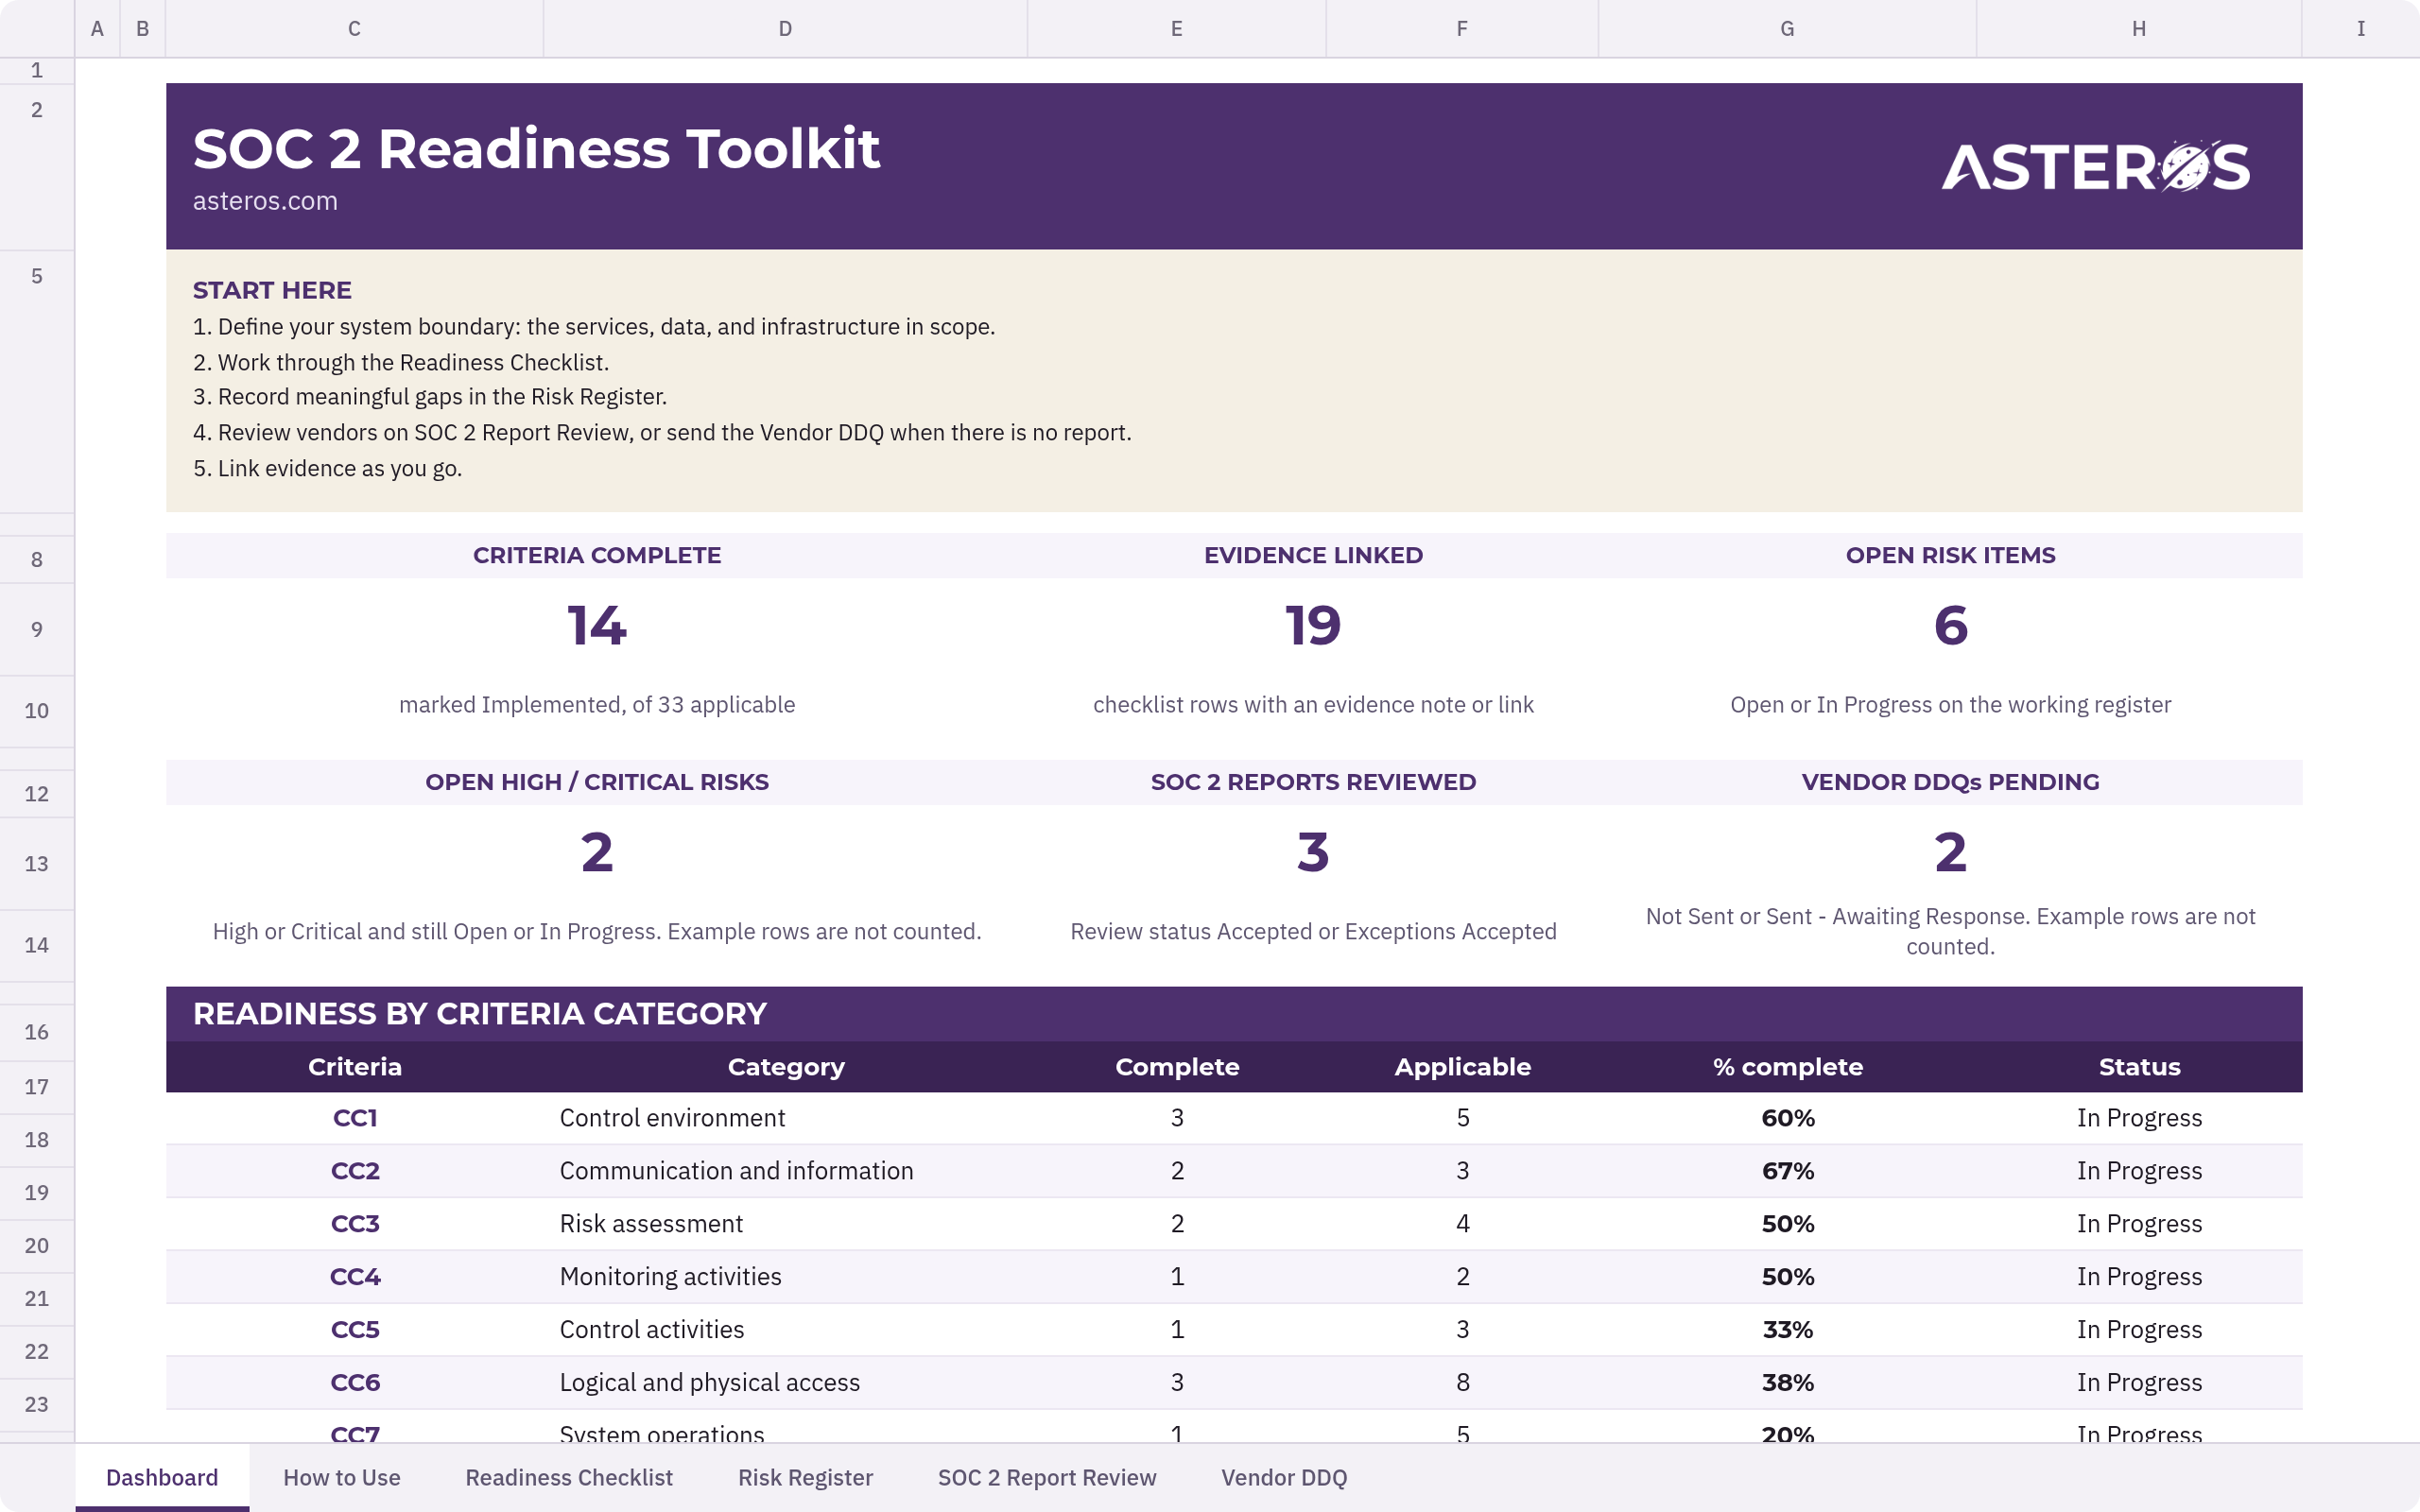
Five tabs that take you from criteria to evidence to vendors, plus a guide that explains each criterion in plain English.
Readiness Checklist
All 33 Security criteria, what each looks like in practice, and the evidence teams typically collect.
Risk Register
Score gaps from 1 to 25, assign owners and dates, and start from example risks that are never counted.
Vendor review
Record what a vendor’s SOC 2 report actually says, or send a 35-question DDQ when there is no report.
Dashboard
Criteria complete, evidence linked, open high-risk items, and vendor reviews pending, updated as you work.
What it is
Pick the format your team already uses
Same content in each. The guide reads well on its own or beside the workbook.
Google Sheets
The same workbook as a copy in your Drive, ready to share with your team.
Make a copyNotion
Linked databases for criteria, risks, and vendors, with owners and dates.
Duplicate in NotionReadiness guide
Every criterion and vendor question, written to read on its own.
Markdown on GitHubNeed the Penetration Test?
The audit asks whether a test was performed. An enterprise security review asks how. Asteros runs manual-first web application pentests based on OWASP ASVS, with one report written for executives, engineers, and auditors, and retesting included at no additional charge.